
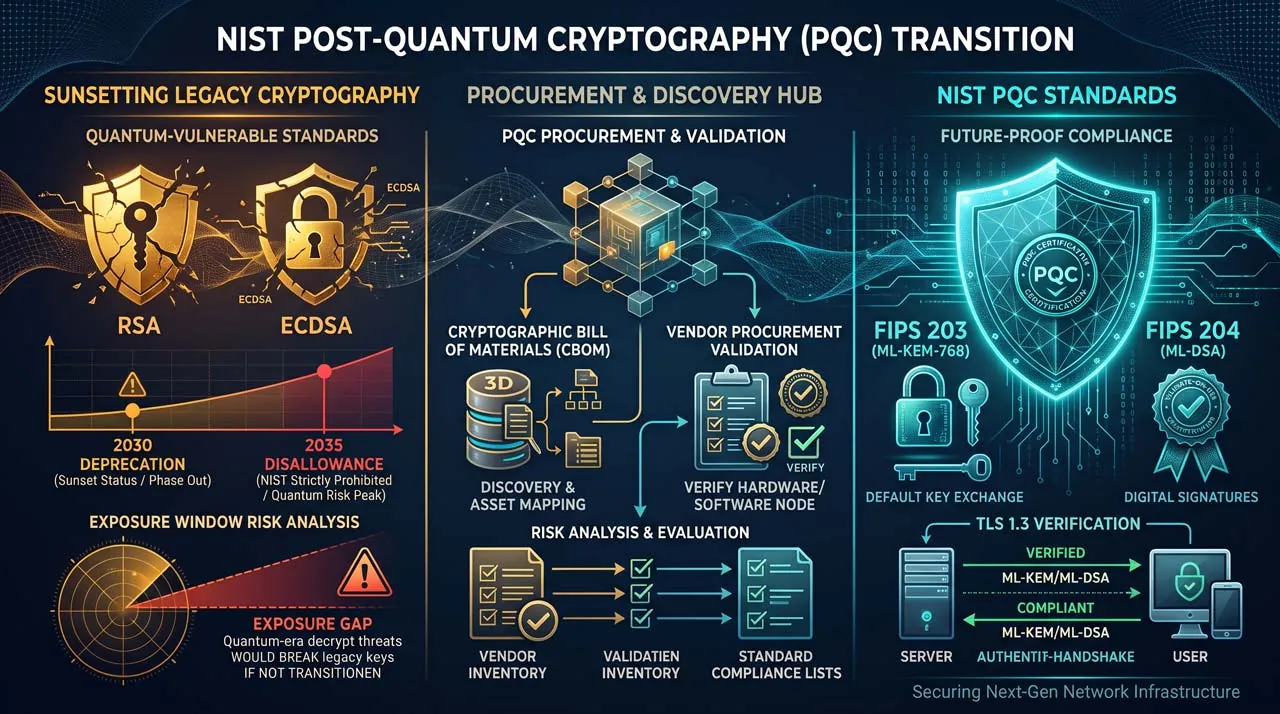
NIST just quietly reset the PQC conversation: this isn’t a crypto team problem anymore, it’s a procurement problem. A new NIST transition report highlighted this week spells out what “post-quantum ready” should actually mean when you’re buying software, hardware, or … Read More
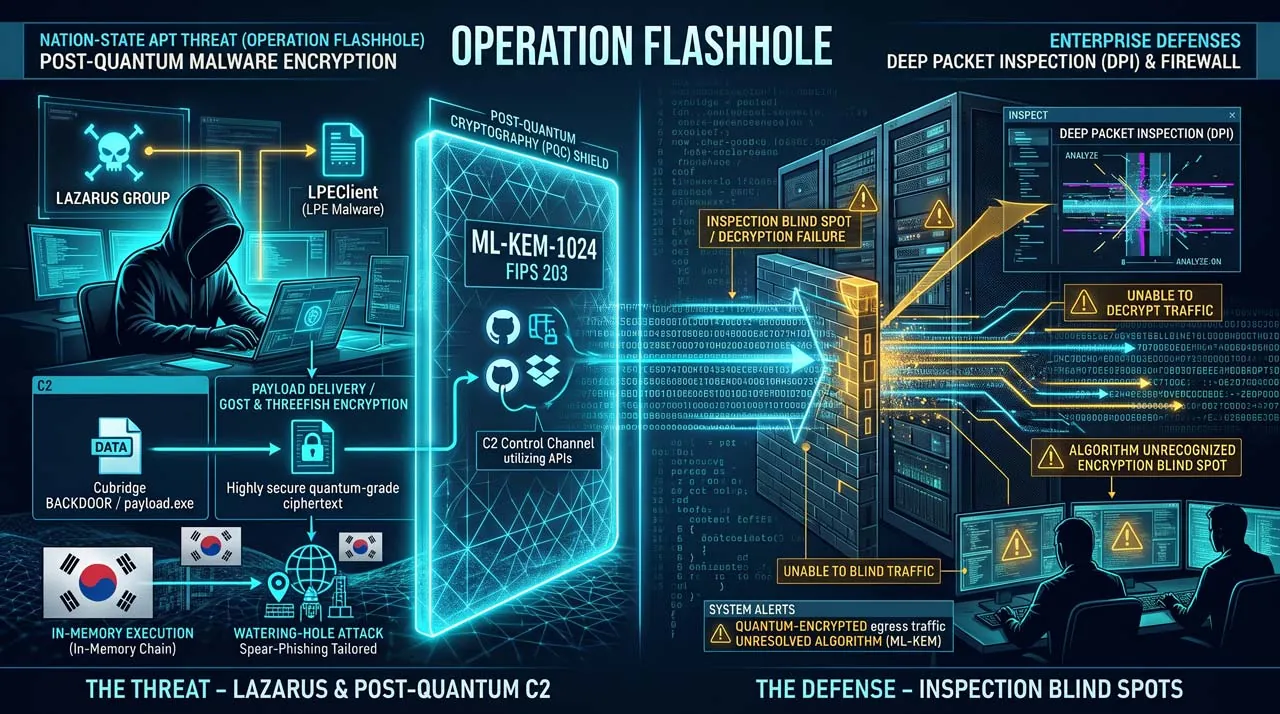
Lazarus is already using ML-KEM-1024 to hide C2 traffic. Is your DPI inspection PQC-aware?
Lazarus beat most Fortune 500 security teams to post-quantum crypto — and it didn’t need a compliance deadline to get there. At Kaspersky’s Security Analyst Summit in Bali this week, GReAT researchers disclosed Operation FlashHole: a Lazarus campaign against South … Read More
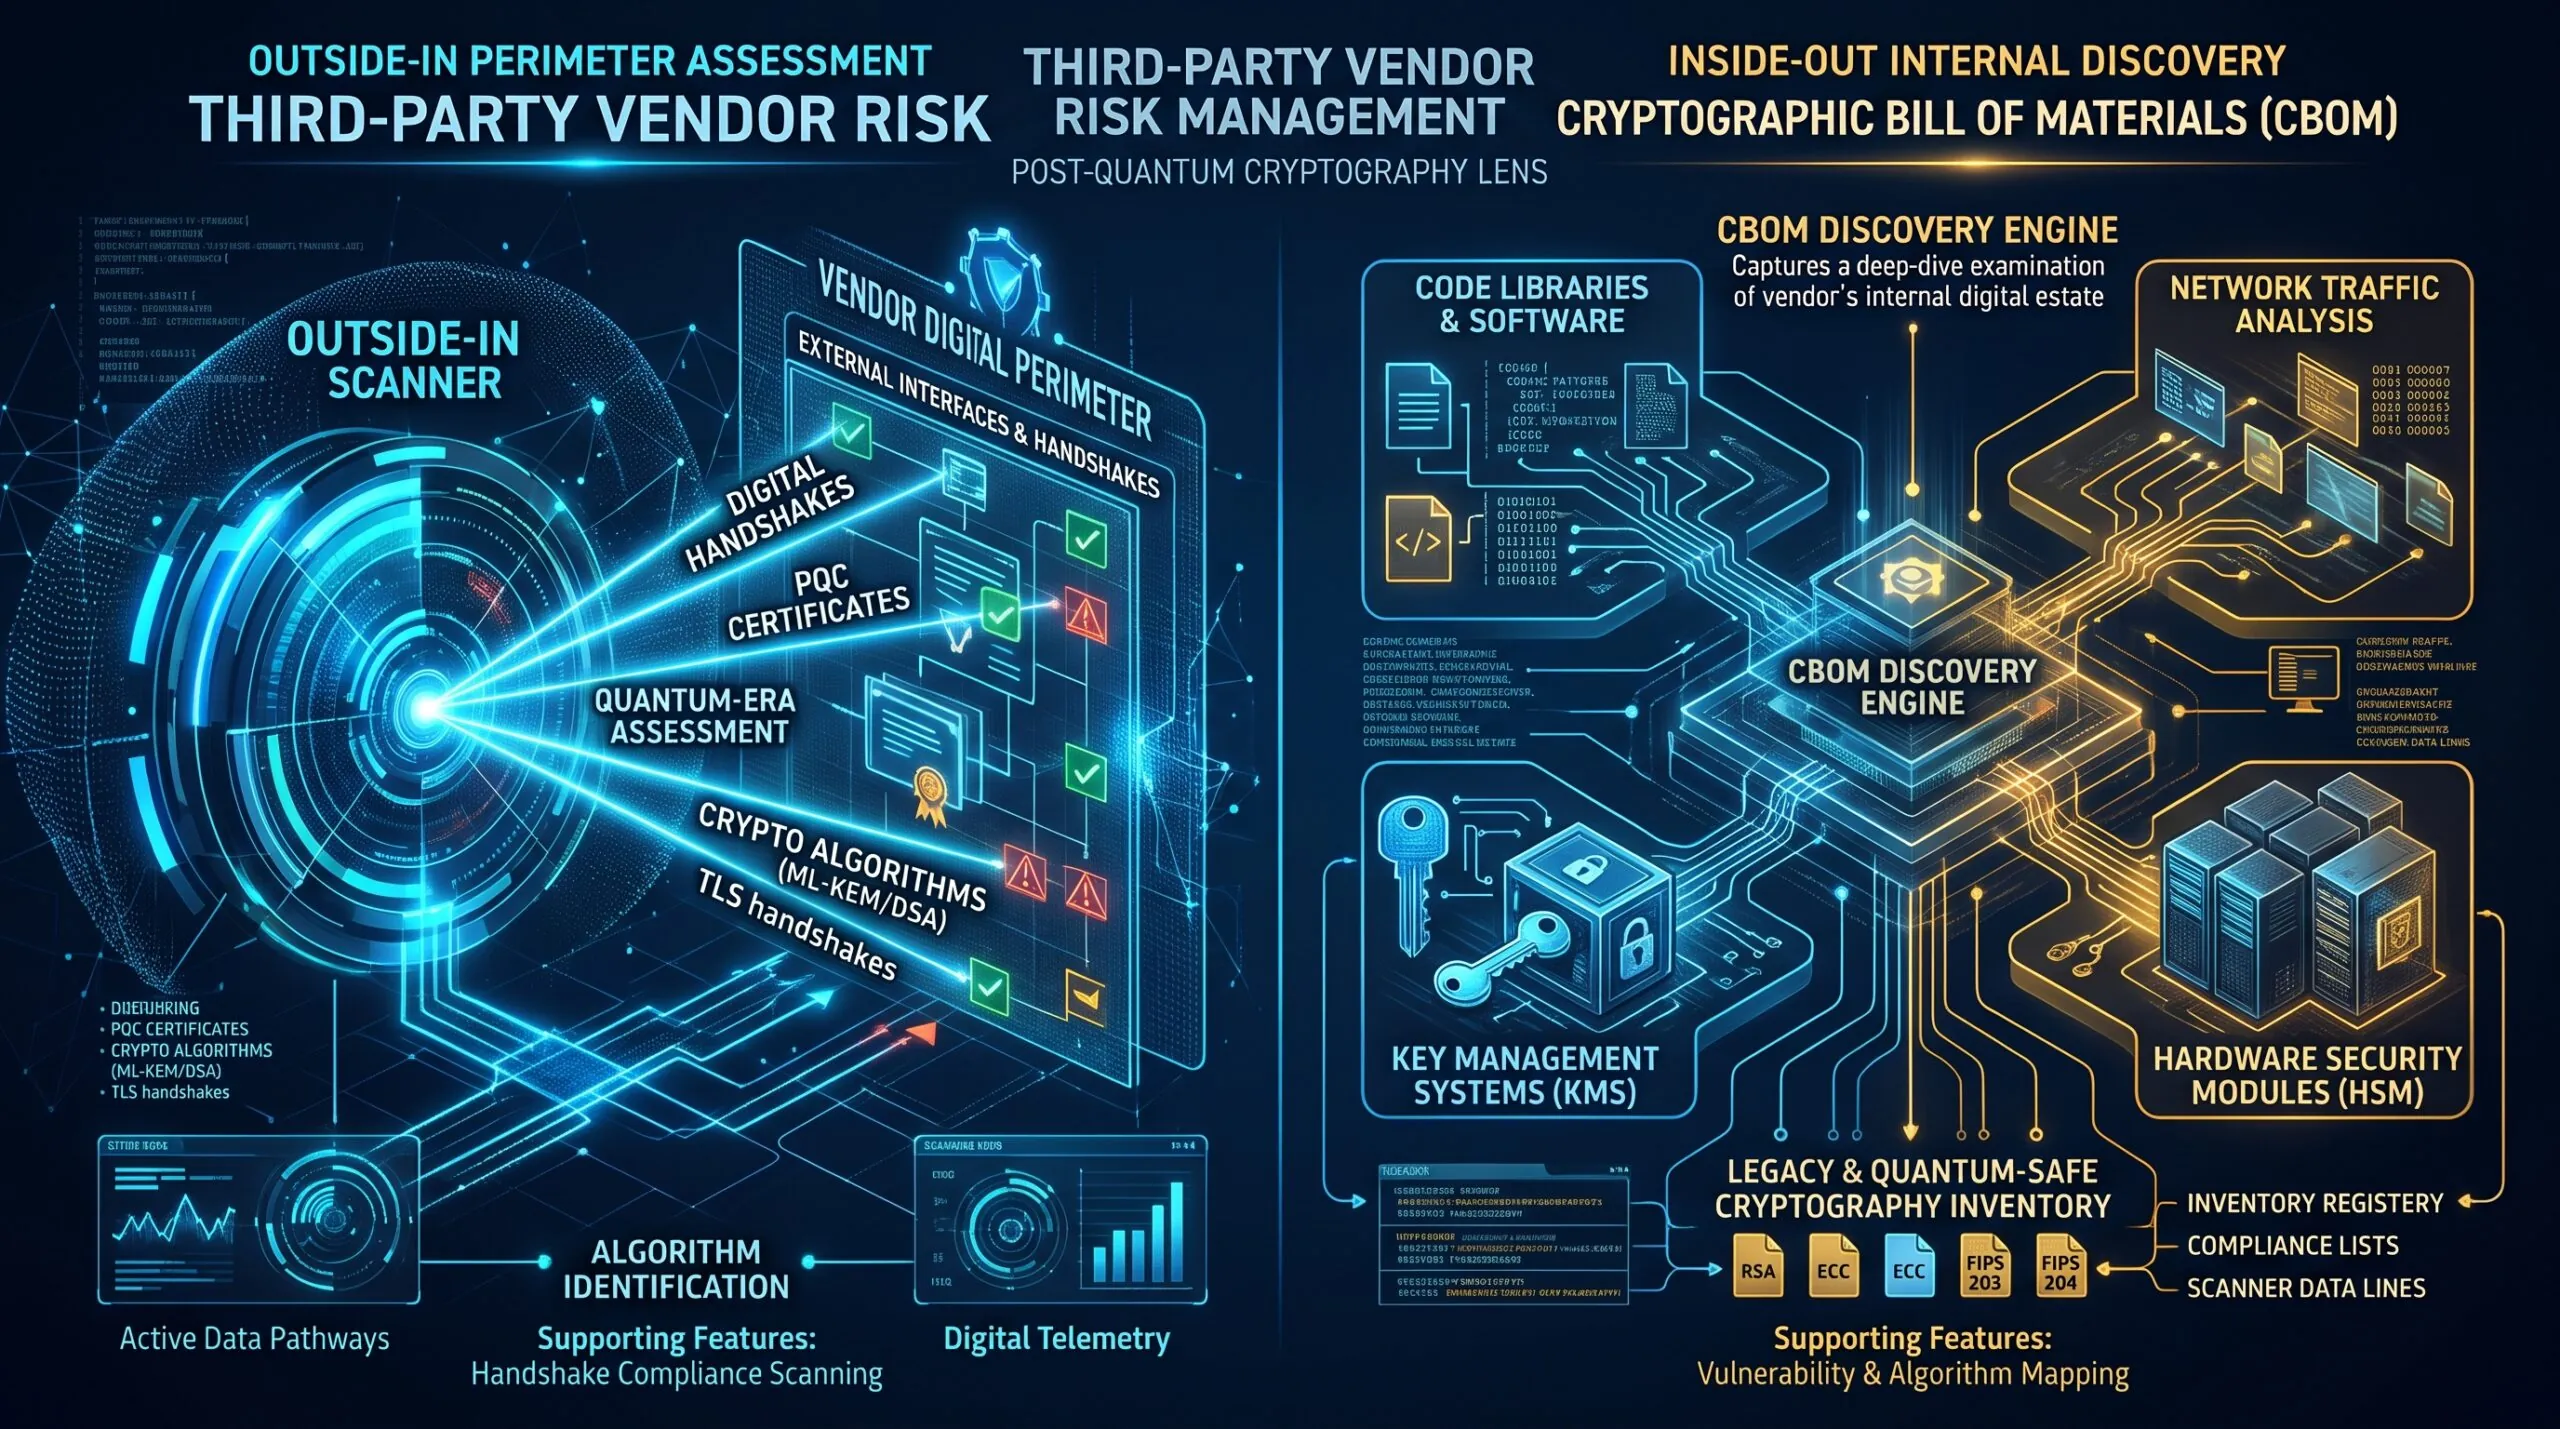
Your PQC migration can be 100% compliant—and your vendors can still bring you down.
Your own PQC migration can be flawless and you can still get burned by a vendor’s TLS certificate sitting on a legacy algorithm you don’t control. Third-party risk just got a quantum lens. On October 21, Black Kite added “Quantum … Read More
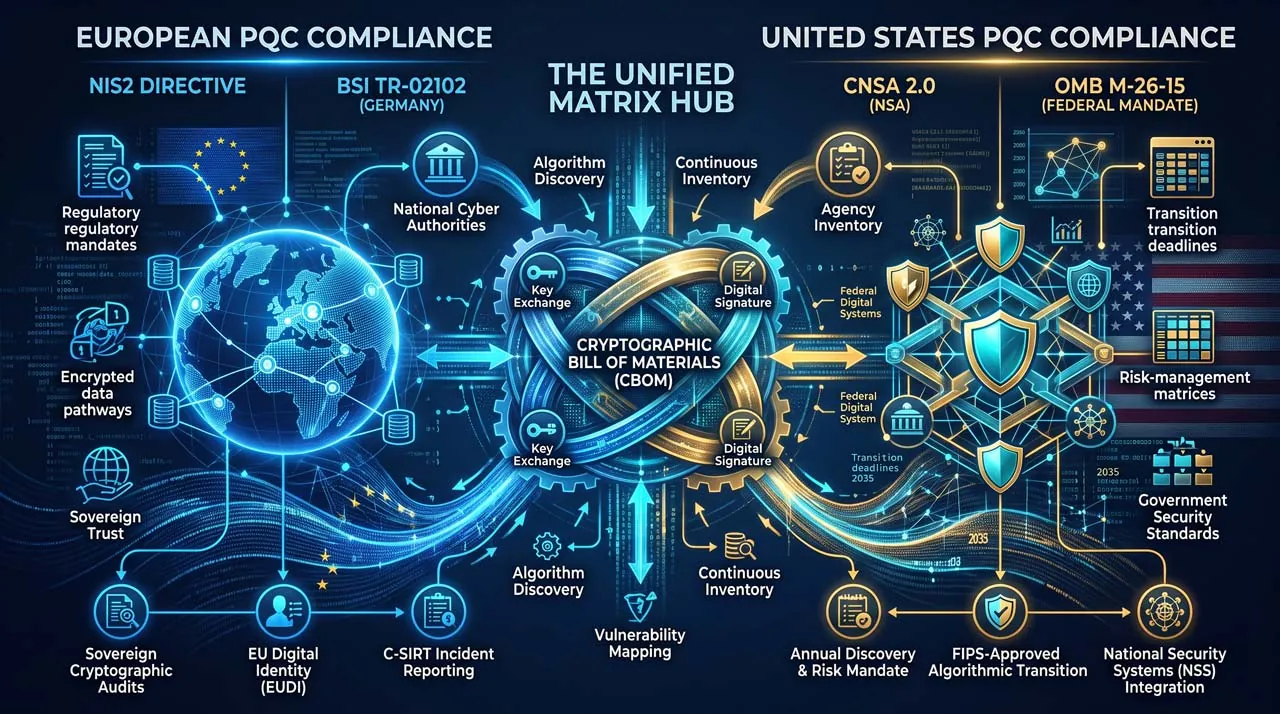
Germany just gave the EU’s post-quantum roadmap legal teeth and a 2026 inventory deadline.
Germany just turned the EU’s post-quantum roadmap into law with teeth — and most US security leaders haven’t noticed. On October 12, Germany’s Interior Ministry (BMI), Digital Ministry (BMDS), and BSI jointly published a national PQC migration guideline implementing the … Read More
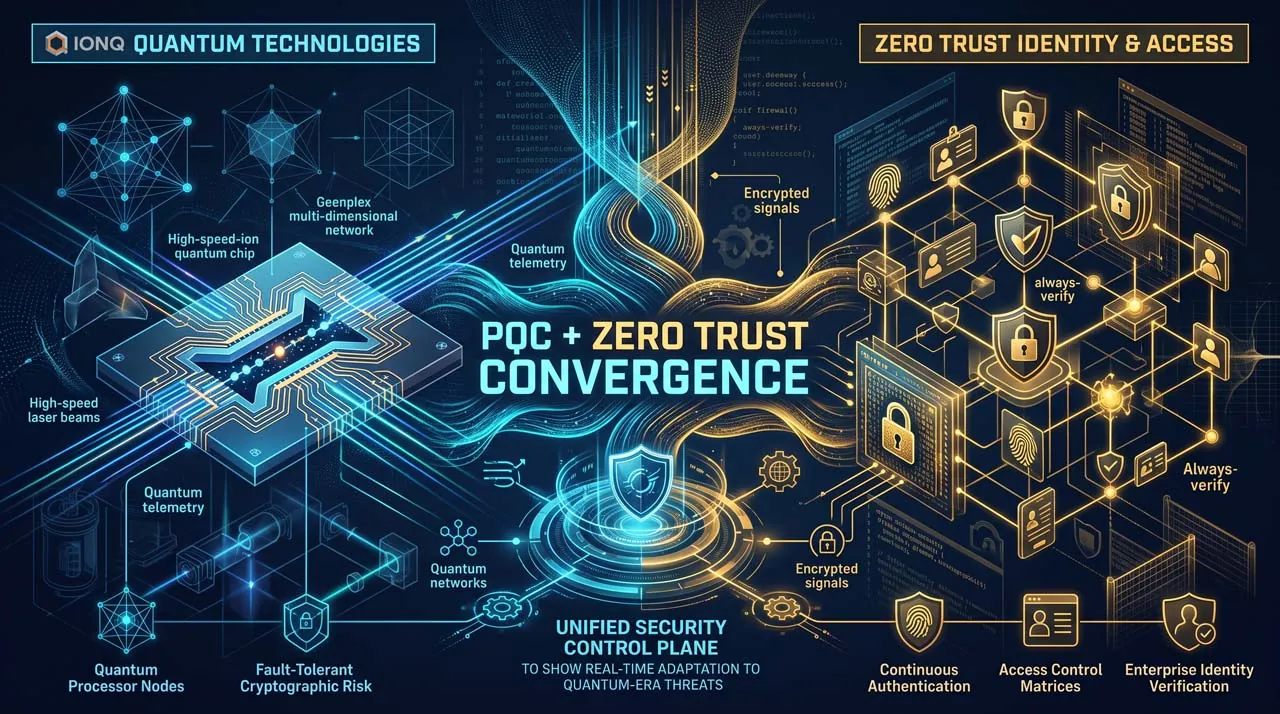
IonQ’s $1.3B acquisition of Elisity proves PQC and Zero Trust are officially converging into one control plane
A quantum computing company just paid up to $1.3 billion to buy a zero-trust access control vendor. If that pairing seems odd, look closer — it’s exactly where enterprise security is headed. On October 9, 2026, IonQ announced it’s acquiring … Read More
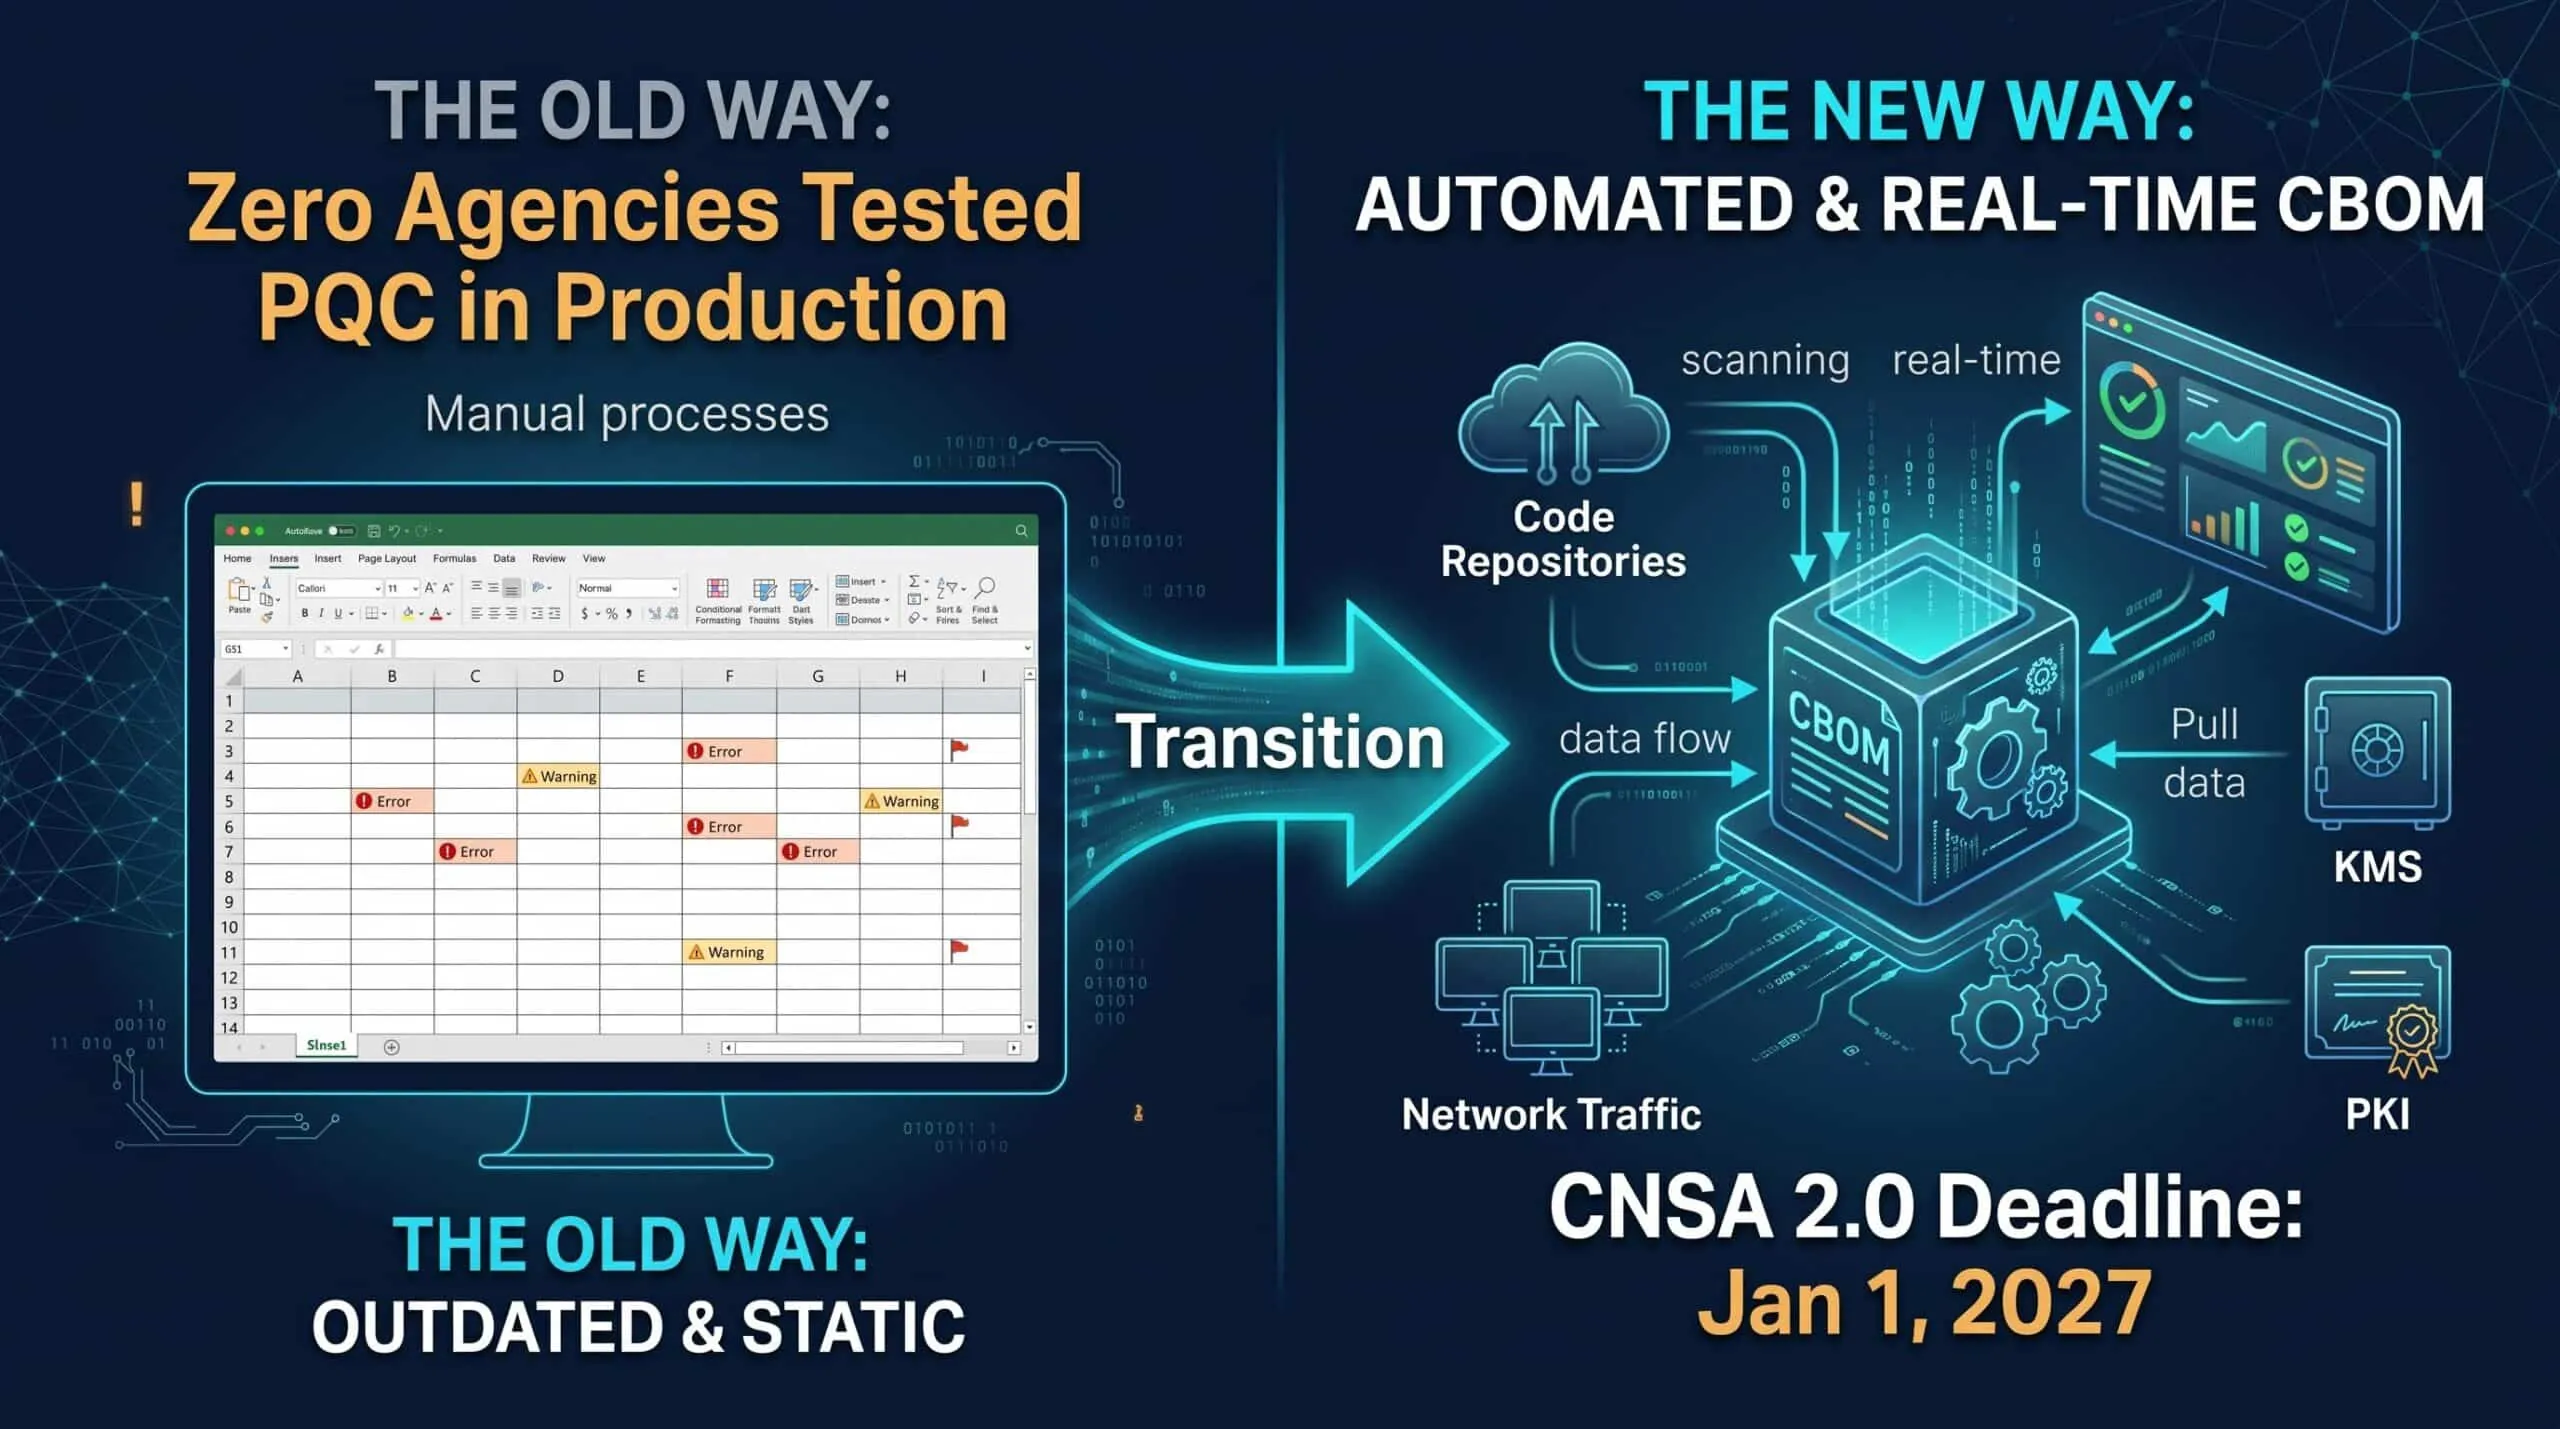
GAO just called out federal quantum readiness. Here’s what enterprise CISOs need to learn from it.
Zero. That’s how many of the 24 largest federal agencies have tested post-quantum cryptography in their own environment, according to a GAO report released October 6. GAO’s audit (GAO-27-108740) checked the 24 CFO Act agencies against three basic PQC-readiness practices … Read More
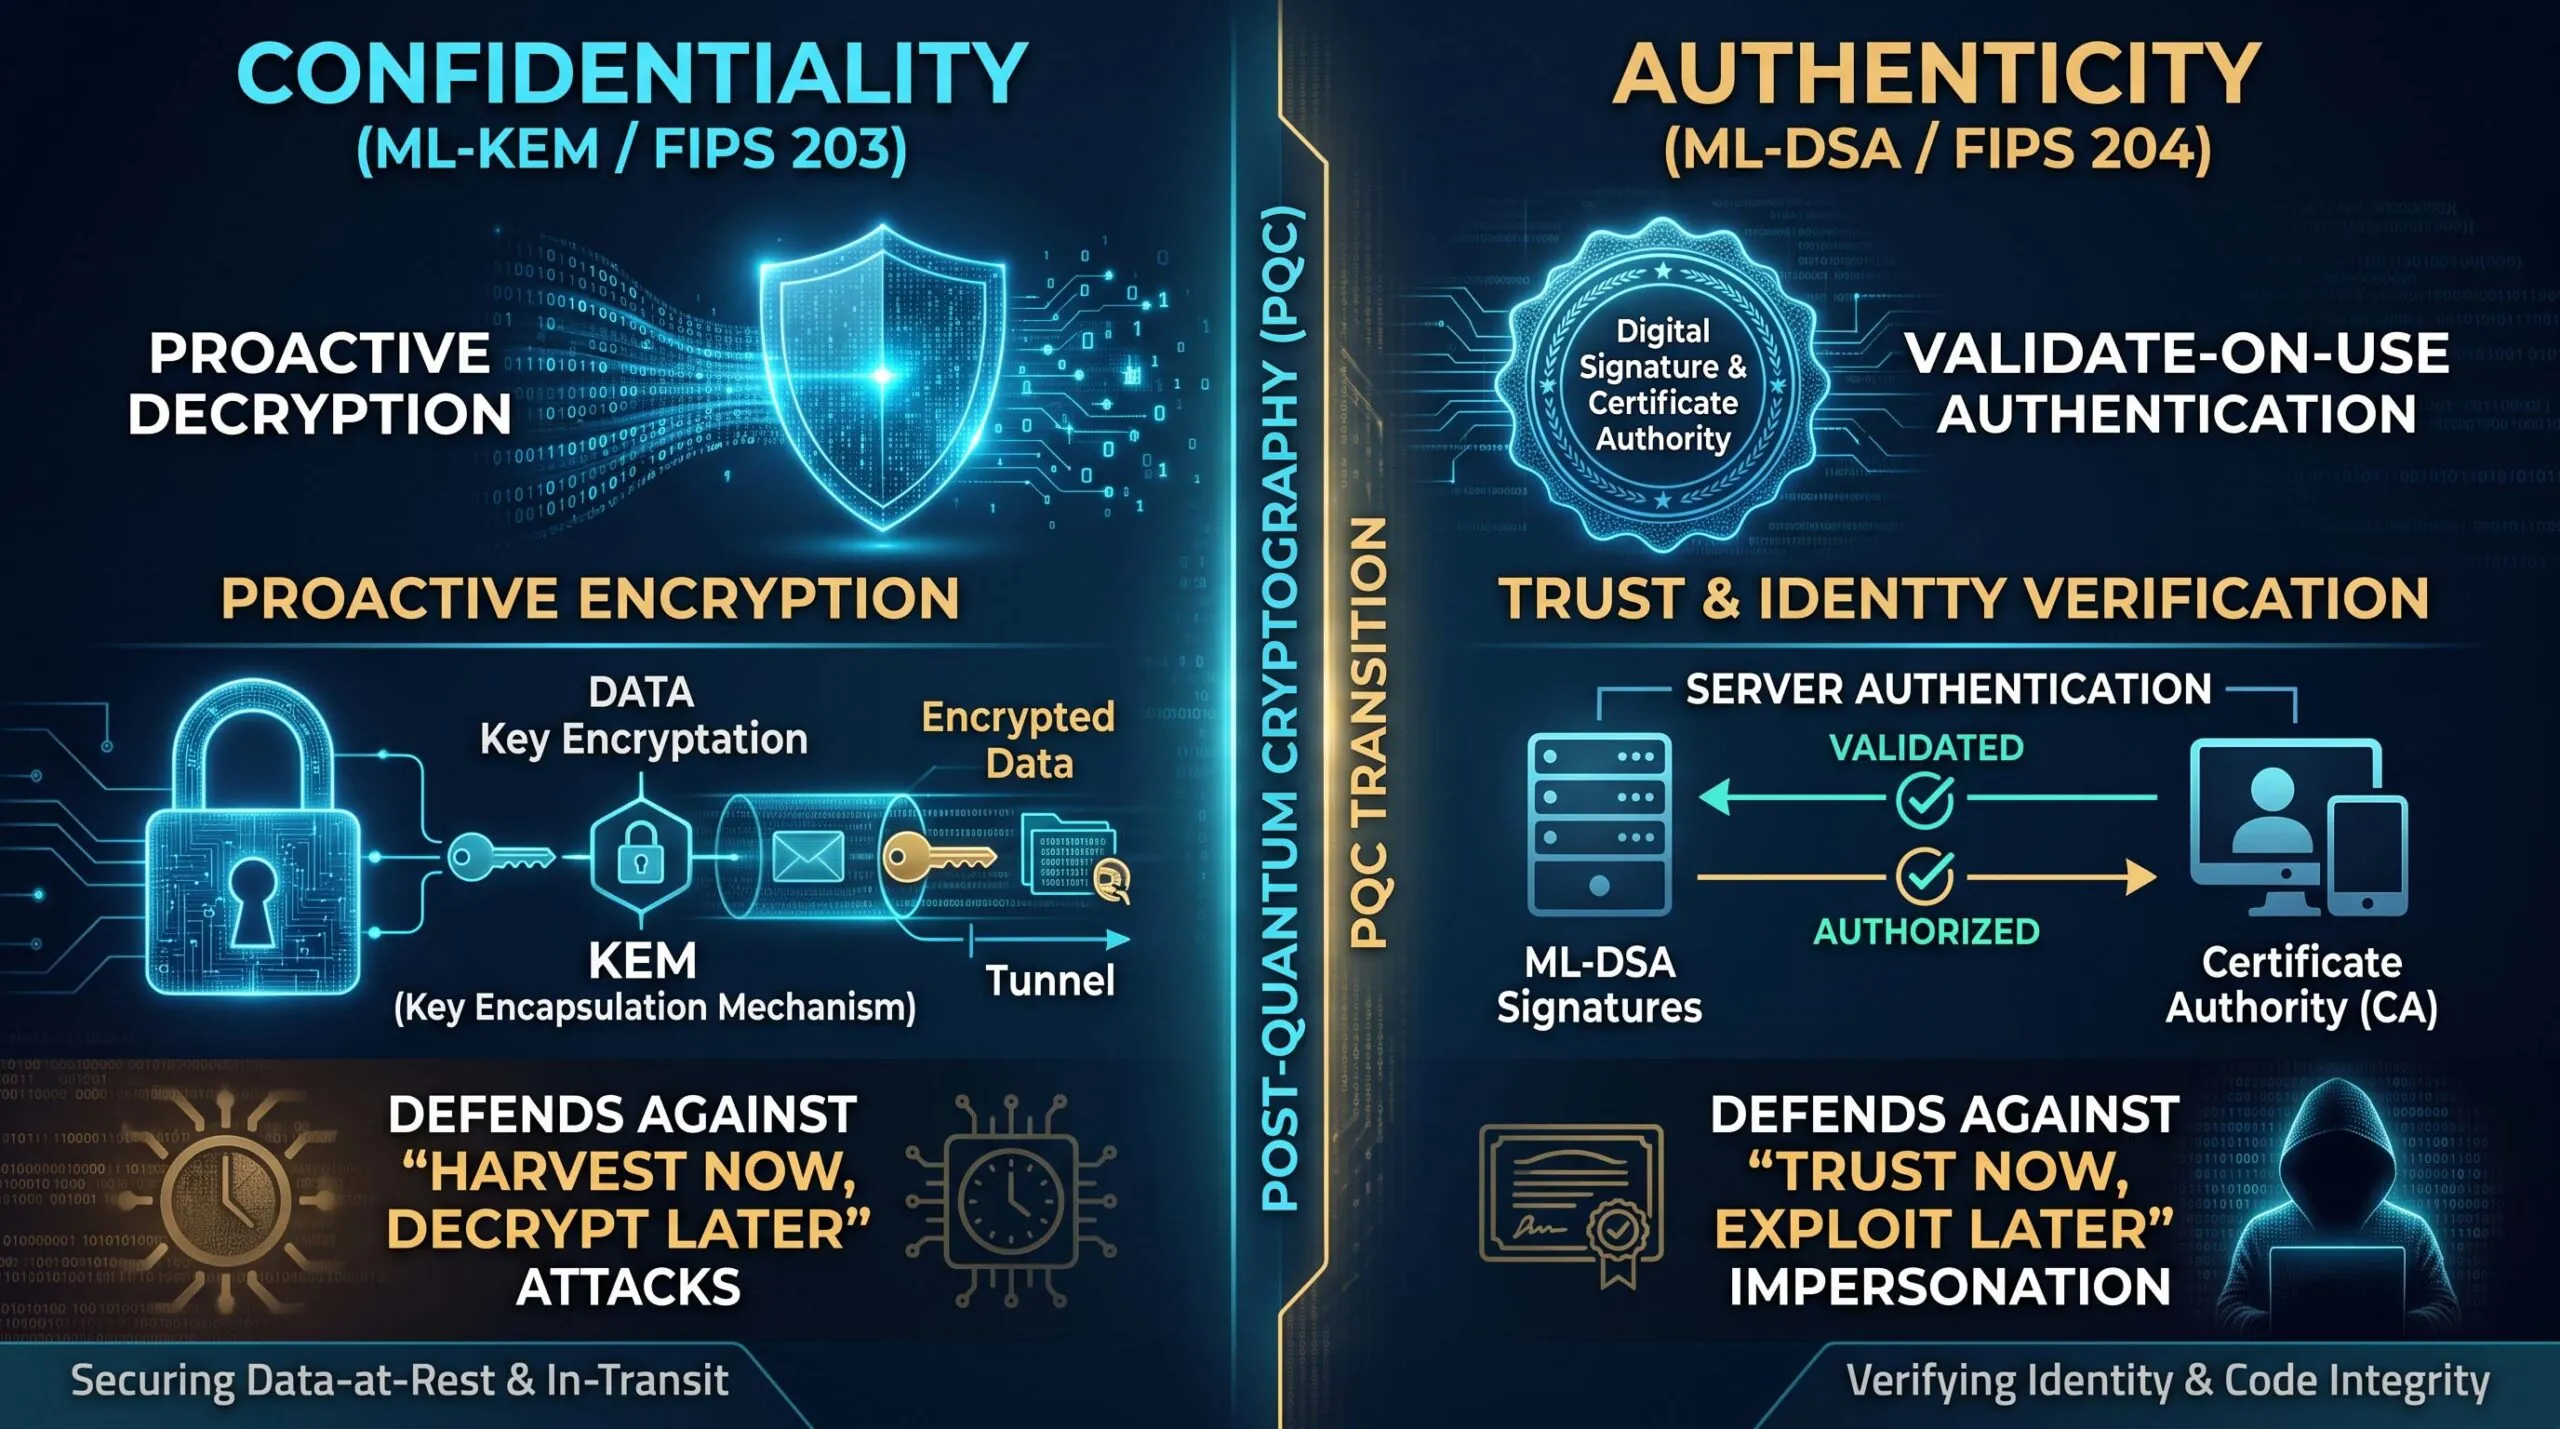
Beyond “Harvest Now, Decrypt Later”: Why the NSA is warning security leaders about “Trust Now, Exploit Later.
Your VPN might already laugh off “harvest now, decrypt later.” That doesn’t mean it can stop a quantum-capable attacker from impersonating your server. On October 7, Surfshark added ML-DSA certificate-based authentication to its WireGuard implementation — completing a migration that … Read More
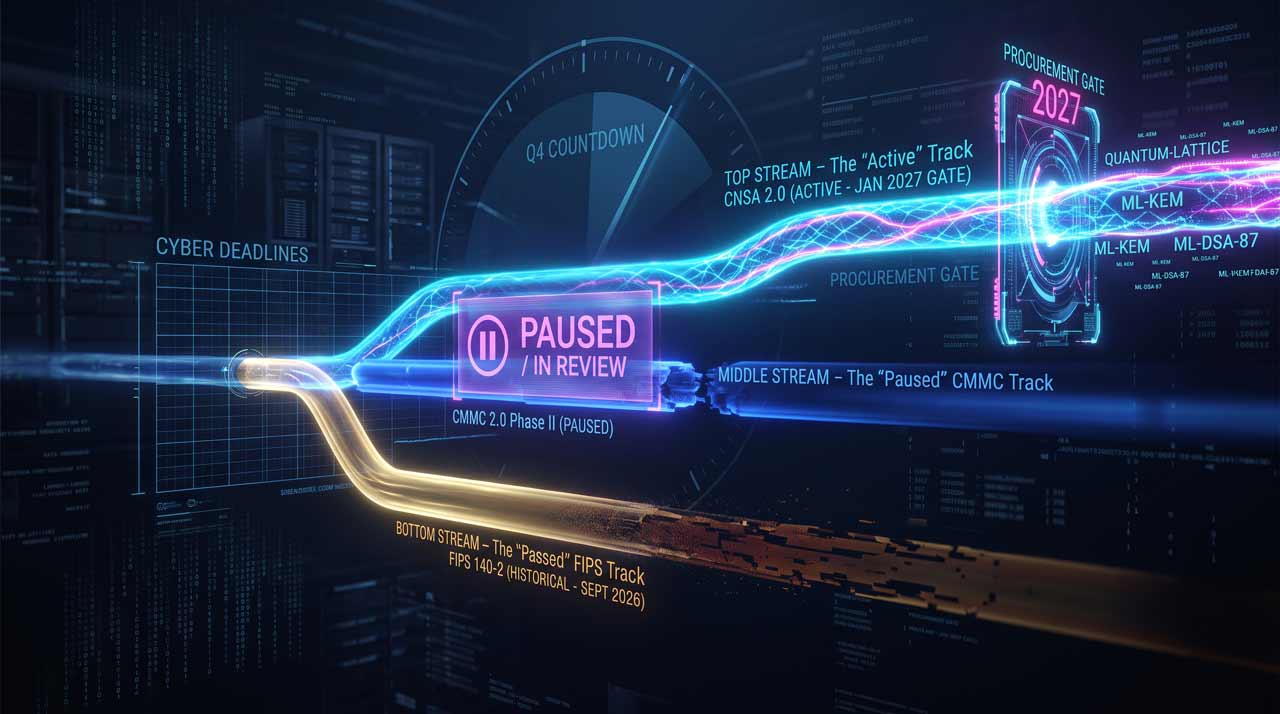
Three PQC Deadlines Hit in 2026. Two Changed. The Deadliest One Didn’t.
Three PQC deadlines hit CISOs’ desks this year. One already passed quietly. One just got paused. The third isn’t moving — and it’s the one with real teeth. FIPS 140-2 → Historical (Sept 21, 2026): NIST’s CMVP moved every FIPS … Read More
The PQC gap sitting right inside your build pipeline
“Harvest now, decrypt later” (HNDL) has dominated the post-quantum cybersecurity narrative for years. But on October 1, the NSA formally framed a second, equally critical threat and most modern cryptographic inventories aren’t equipped to catch it. Here’s how the NSA … Read More
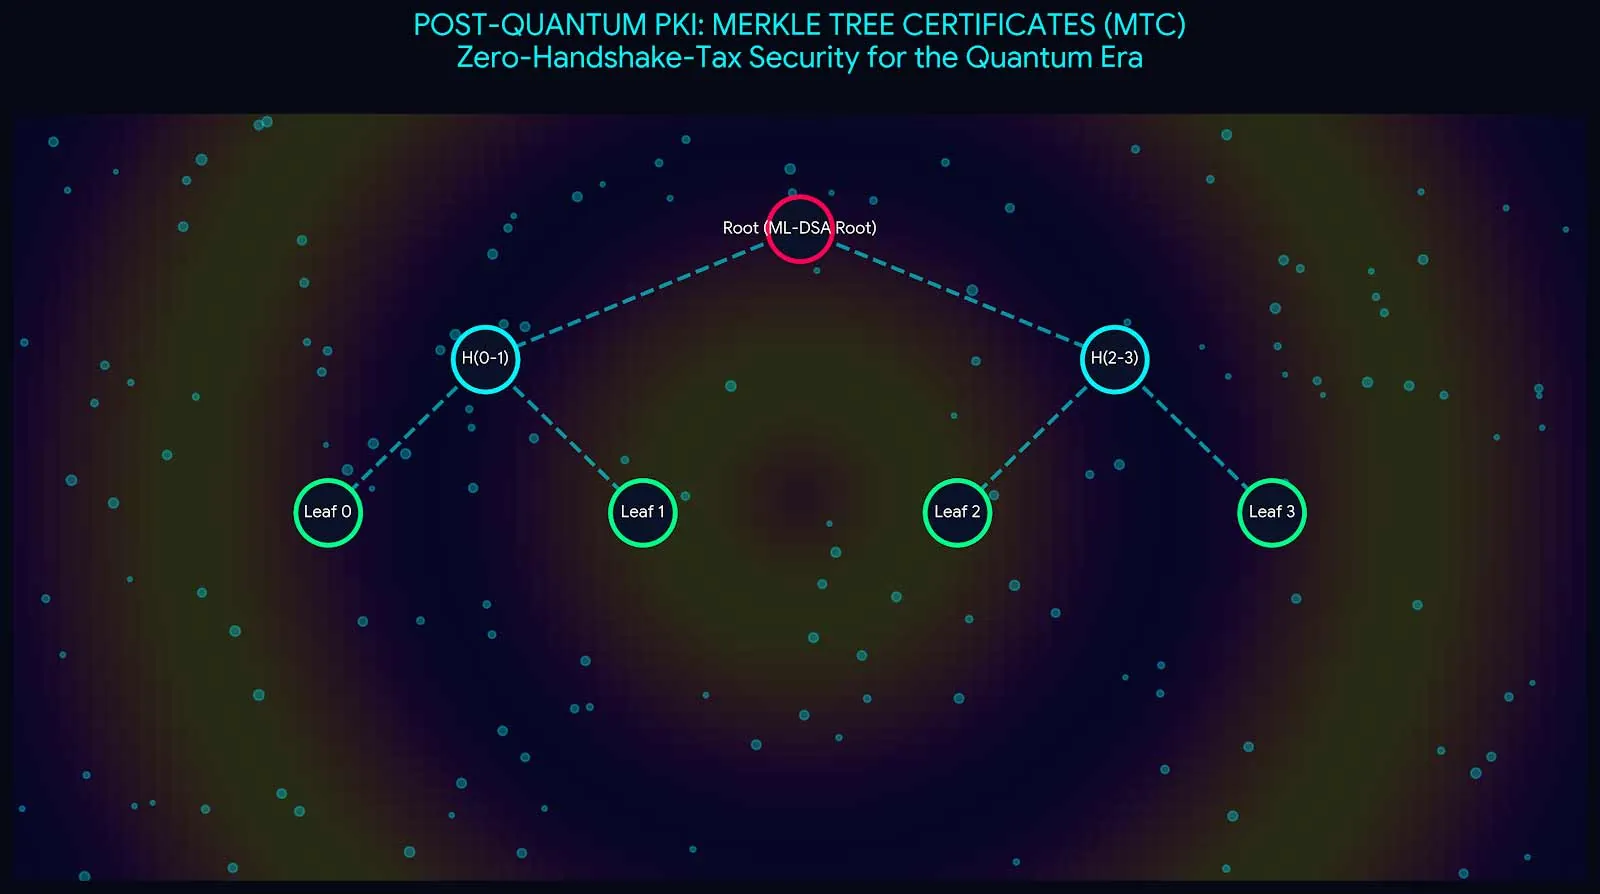
The Public Web Is Moving to Post-Quantum CAs. Is Your Infrastructure Ready?
Every certificate securing HTTPS today runs on RSA or ECDSA math that quantum computers will eventually break. On September 29, Cloudflare said it’s becoming a public Certificate Authority built for what comes next — and the design shows exactly how … Read More