
GAO’s audit (GAO-27-108740) checked the 24 CFO Act agencies against three basic PQC-readiness practices — inventory, cost estimation, testing — and found that not one agency fully addressed all three. The breakdown is worse than the headline:
Inventory: Only 1 of 24 agencies fully built a prioritized cryptographic inventory, and 1 had no inventory at all. 19 of 24 use no automated discovery tools — one agency with more than 4 million endpoints has no documented plan to even start.
Expertise: 18 of 24 agencies reported lacking cryptography expertise, with no plan in place to close the gap.
Cost: No agency fully assessed migration funding. OMB and ONCD now put the governmentwide price tag near $7.1 billion — a large share of it for replacing legacy systems that can’t run PQC at all, not just swapping algorithms.
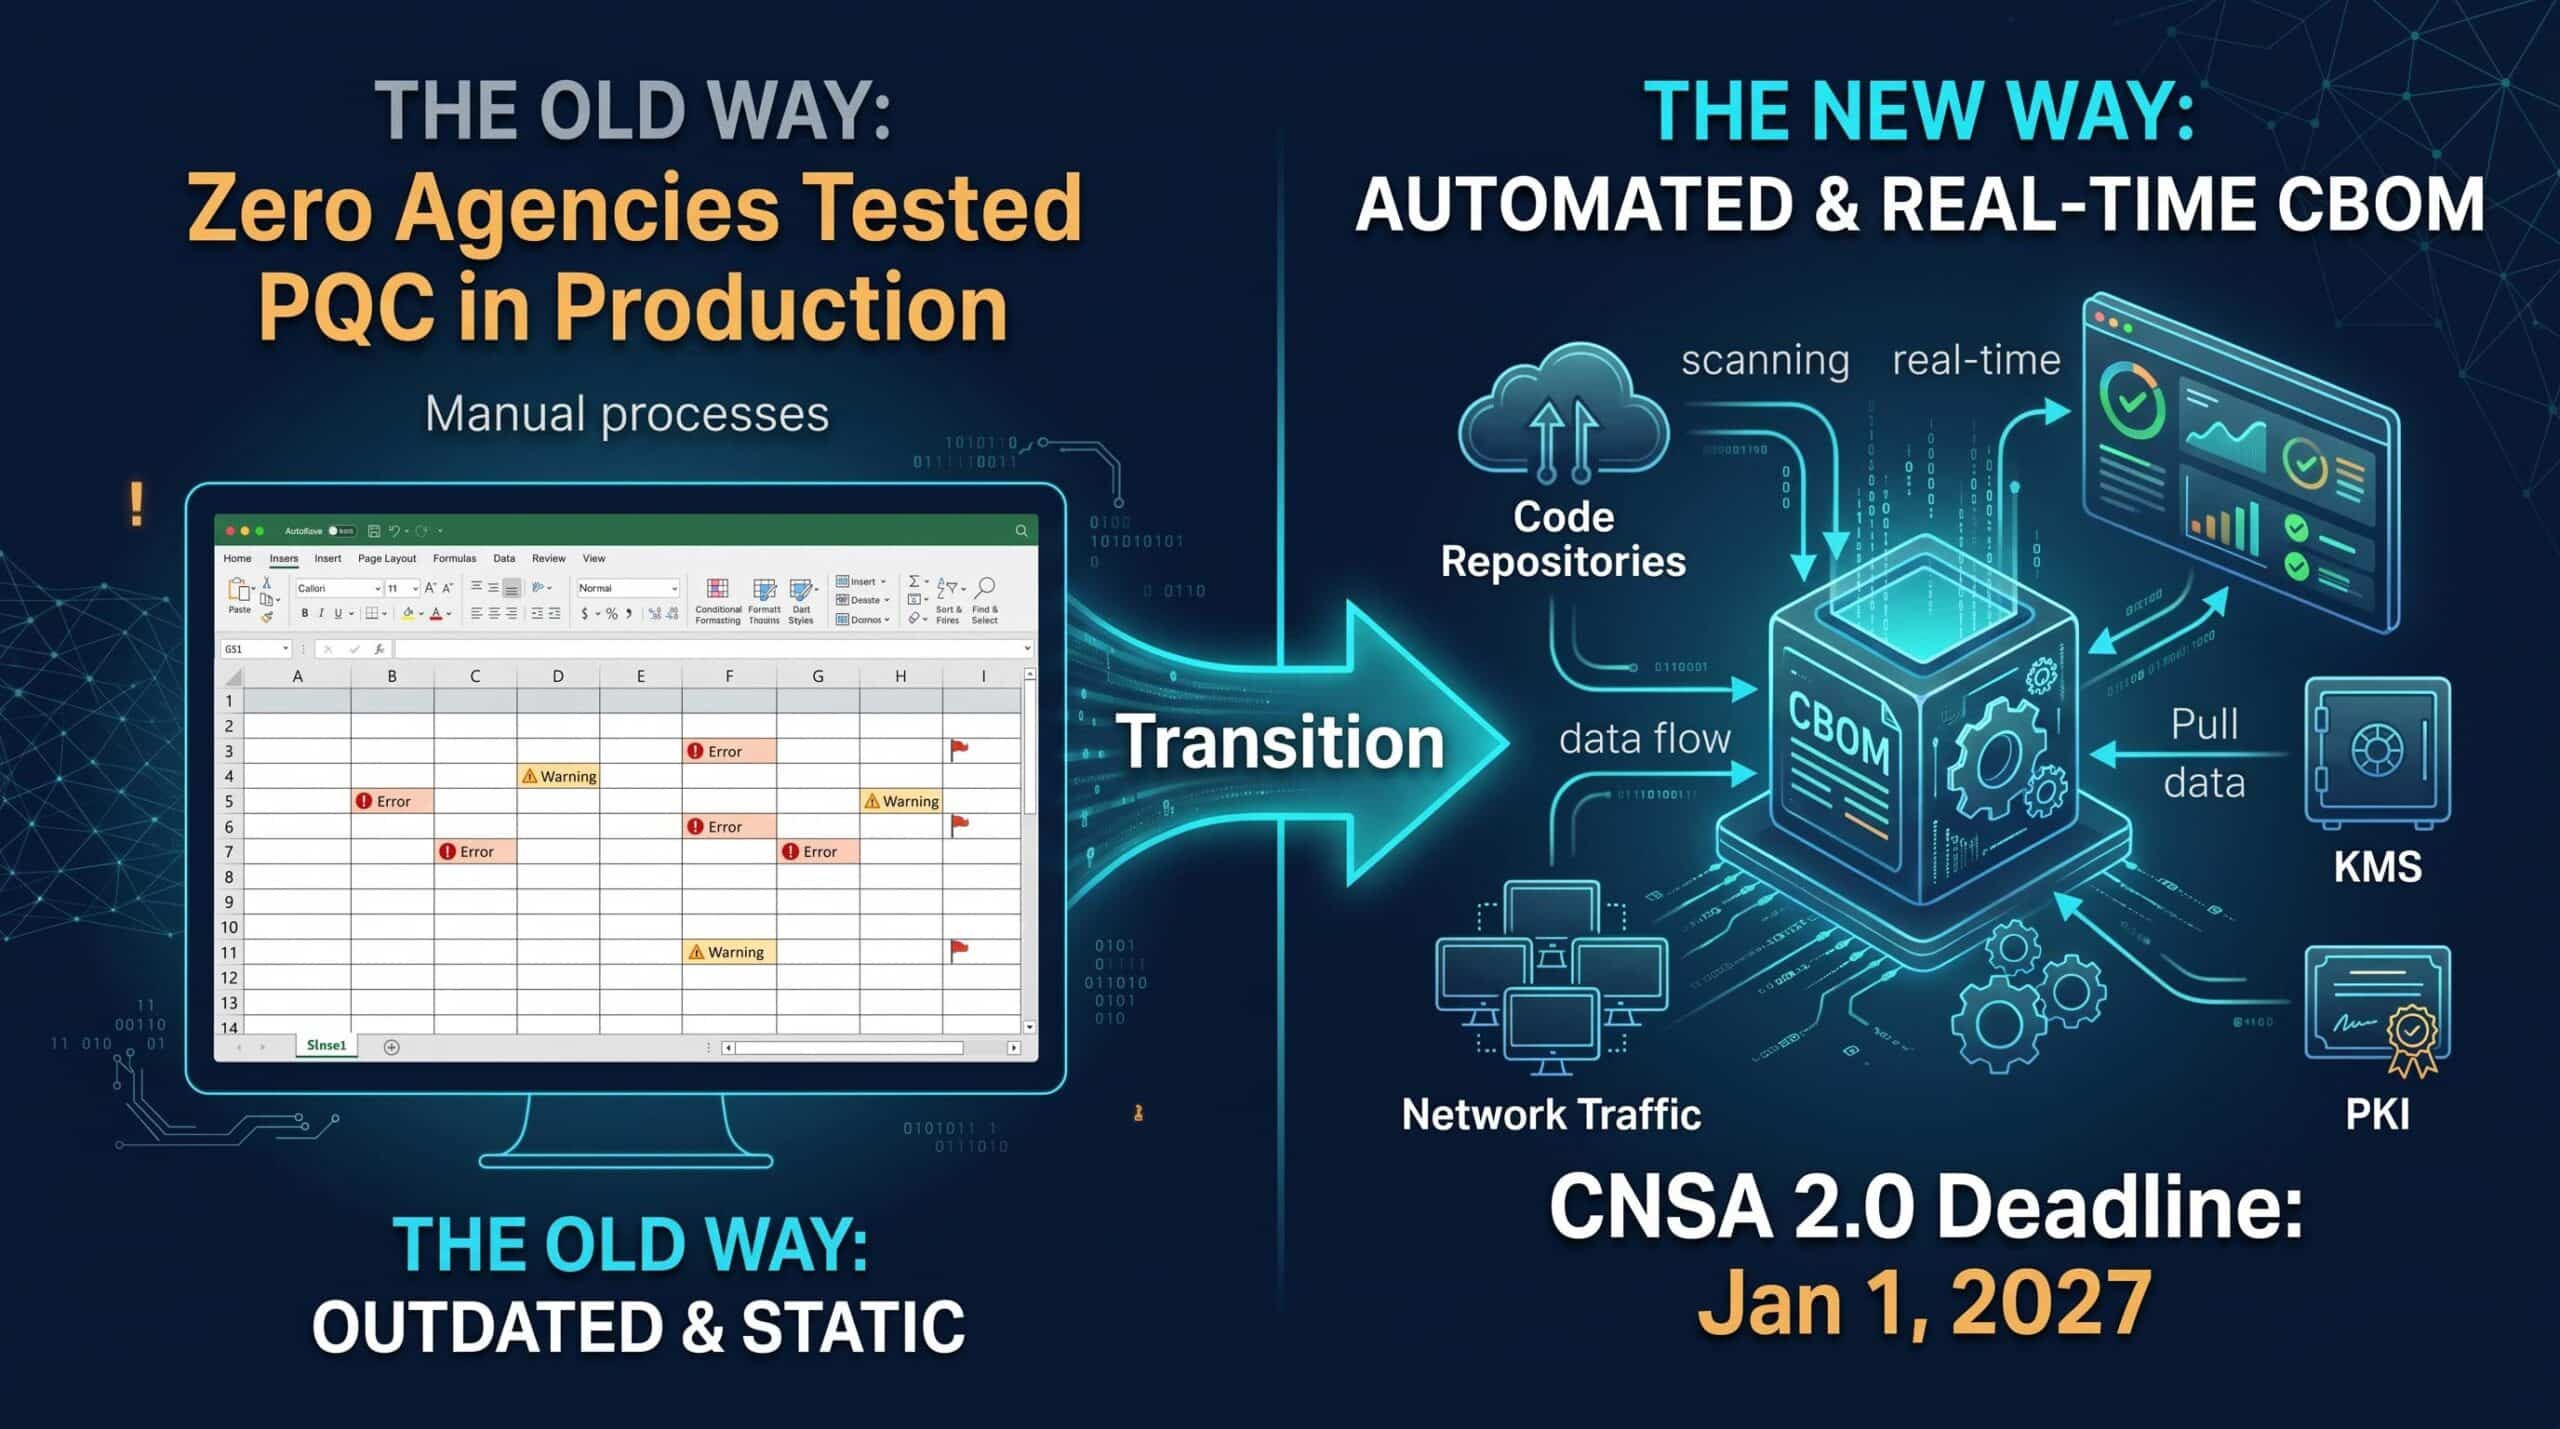
The GAO just released a reality check on federal quantum readiness: Zero agencies have tested Post-Quantum Cryptography in their own environments.
Sixteen agencies argued it’s “too early.” The GAO explicitly disagreed, pushing back that testing now is entirely practical given where vendor support stands today.
Here’s the hard truth: CNSA 2.0’s January 1, 2027 procurement gate isn’t going to pause while teams finish manually mapping their systems.
You simply can’t migrate what you haven’t discovered—and a static spreadsheet will never scale across millions of endpoints, code repos, and legacy workloads.
We see this exact gap every day when auditing enterprise and financial-sector environments. The struggle isn’t a lack of awareness; it’s a lack of visibility.
If asked today, how confident are you that your cryptographic inventory actually matches what’s actively running in production?
This exact disconnect is why we built QuantVision’s CBOM engine. Instead of relying on static spreadsheets no one fully trusts, it automates discovery across network traffic, build artifacts, KMS, and PKI—mapping everything directly to FIPS 203/204/205 and CNSA 2.0 standards.
The transition to PQC is a live operational challenge, not a future exercise.
Sources & Further Reading:
- GAO Report (Oct 6, 2026): “Quantum Computing: Federal Actions Needed to Prepare for Emerging Cyber Threat” (GAO-27-108740)
- The Quantum Insider Coverage (Oct 7, 2026): Federal Quantum Readiness Falls Short as Agencies Face Skills Gaps
#PostQuantumCryptography #PQC #CryptoAgility #CISO #CNSA2 #NIST #Cybersecurity #RiskManagement #QuantumSafe #CBOM