
RFC 10024, published August 10, 2026, formalizes three hybrid mechanisms for TLS 1.3, pairing ML-KEM (FIPS 203) with classical elliptic curve exchange so a break in either the lattice math or the curve math alone doesn’t break the session: The … Read More
Author Archives: Qubit Guard
ML-KEM is mathematically sound. The library shipping it wasn’t — and for eight months, nobody noticed
ML-KEM is mathematically sound. The library shipping it wasn’t — and for eight months, nobody noticed. In August, researchers (including Anthropic’s Nicholas Carlini) disclosed two implementation flaws in wolfSSL’s hand-optimized ML-KEM decapsulation code. Both are now patched, but the mechanism … Read More
October 22, 2026 isn’t a typo — it’s 28 days out, and it’s the date every U.S. federal civilian agency owes OMB a completed post-quantum migration plan
Here’s what changed and why it matters even if you’re not a federal CISO: The mandate. OMB Memorandum M-26-15, issued June 24 under Executive Order 14412, gave civilian agencies 120 days to submit PQC migration plans — risk-based system prioritization, … Read More
A spreadsheet listing your RSA certificates is not a Cryptographic Bill of Materials. It’s a liability with a fancier name
Entrust recently expanded its Cryptographic Security Platform specifically to address this gap—adding CBOM import/export, dependency mapping, and Ansible-based certificate automation. The vendor matters less than the broader industry signal: static crypto inventories are getting deprecated in favor of systems that connect … Read More
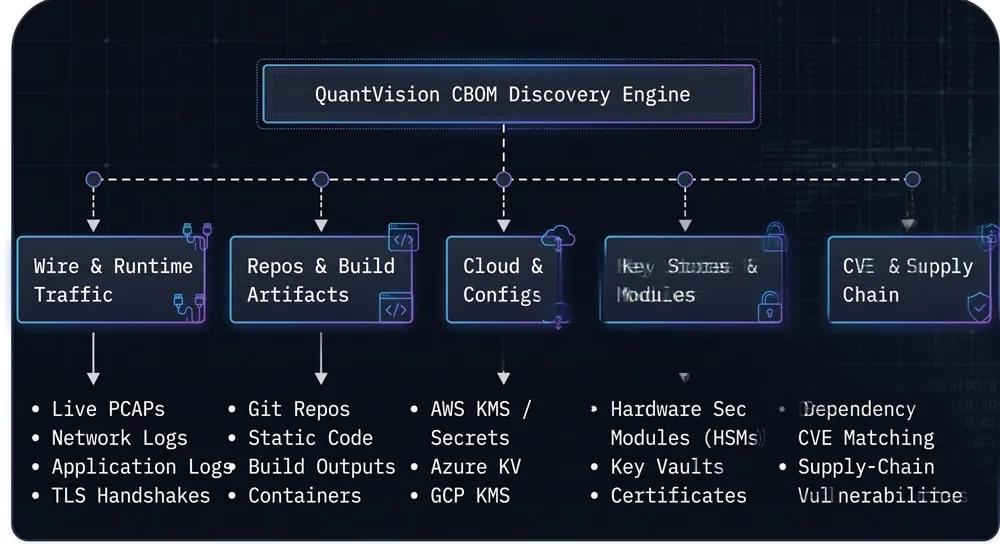
Why Single-Point Scanners Miss 50% of Your Crypto—And How QuantVision Fixes It
As organizations brace for the Post-Quantum Cryptography (PQC) transition mandated by NIST and global compliance frameworks, one foundational task stands in every CISO’s way: Building a complete Cryptographic Bill of Materials (CBOM). You cannot migrate what you cannot see. But … Read More
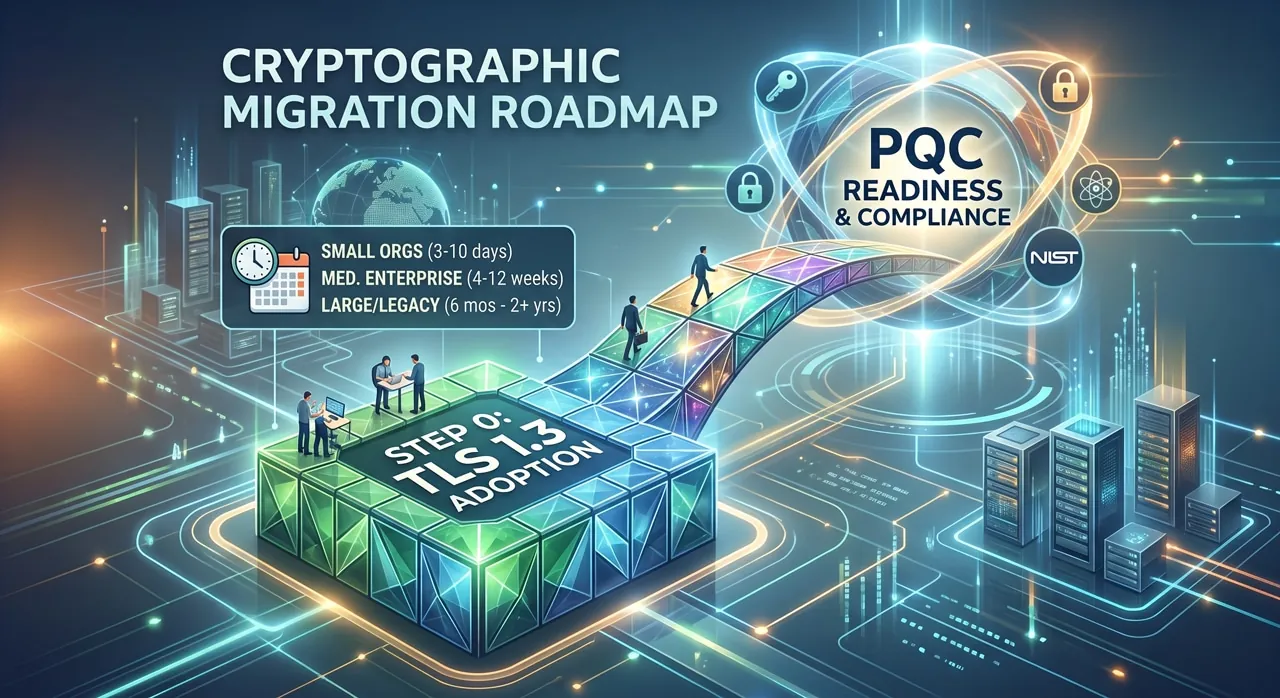
You can’t get to PQC without TLS 1.3.
If you are leading cybersecurity or post-quantum readiness efforts, this isn’t just a best practice—it is the foundational prerequisite for quantum resilience. As organizations gear up for Post-Quantum Cryptography (PQC) migration, many overlook a critical dependency: your network layer must … Read More
Navigating Post-Quantum Cryptography in Practice: Lessons from OpenSSL and Enterprise Deployment
The migration to Post-Quantum Cryptography (PQC) is transitioning rapidly from theoretical standardization to real-world software integration. For enterprise engineering teams and CISOs, understanding how foundational cryptographic libraries implement PQC—and how these changes impact network performance—is critical to building a secure, … Read More
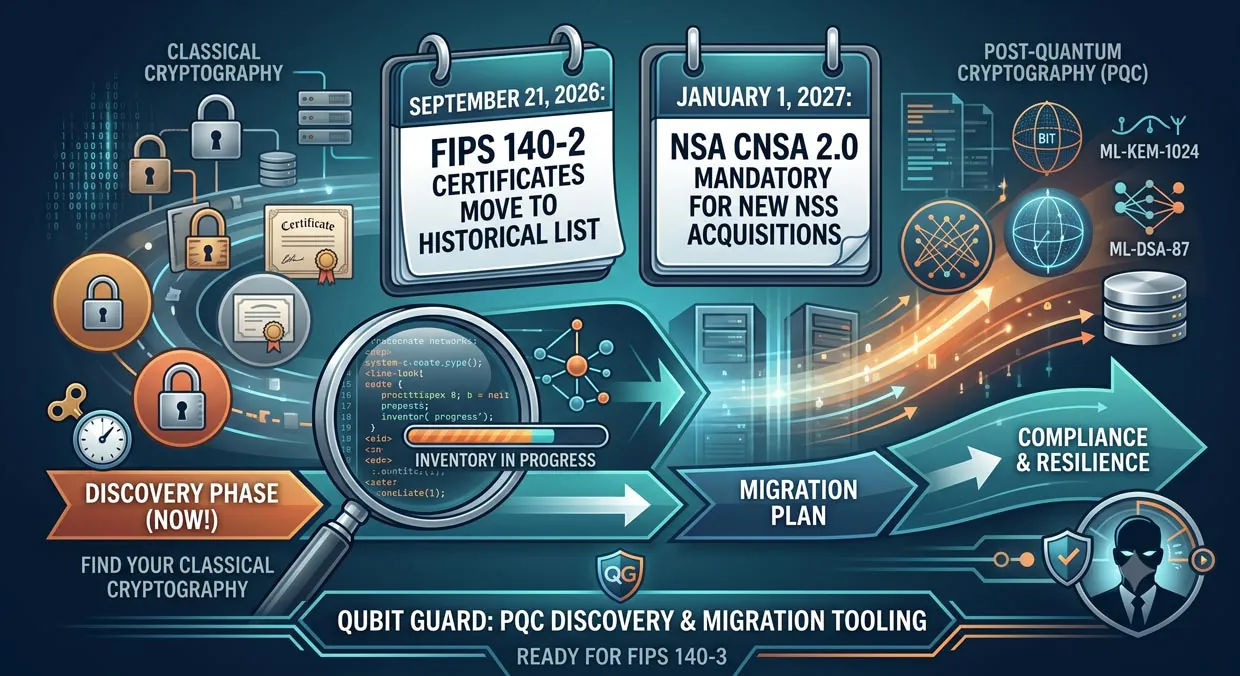
Two dates that should be on every CISO’s calendar right now
📅 September 21, 2026 — NIST’s CMVP moves every active FIPS 140-2 certificate to the Historical List. It doesn’t mean your crypto module is broken. It means federal agencies can no longer cite it to justify a new procurement. If … Read More
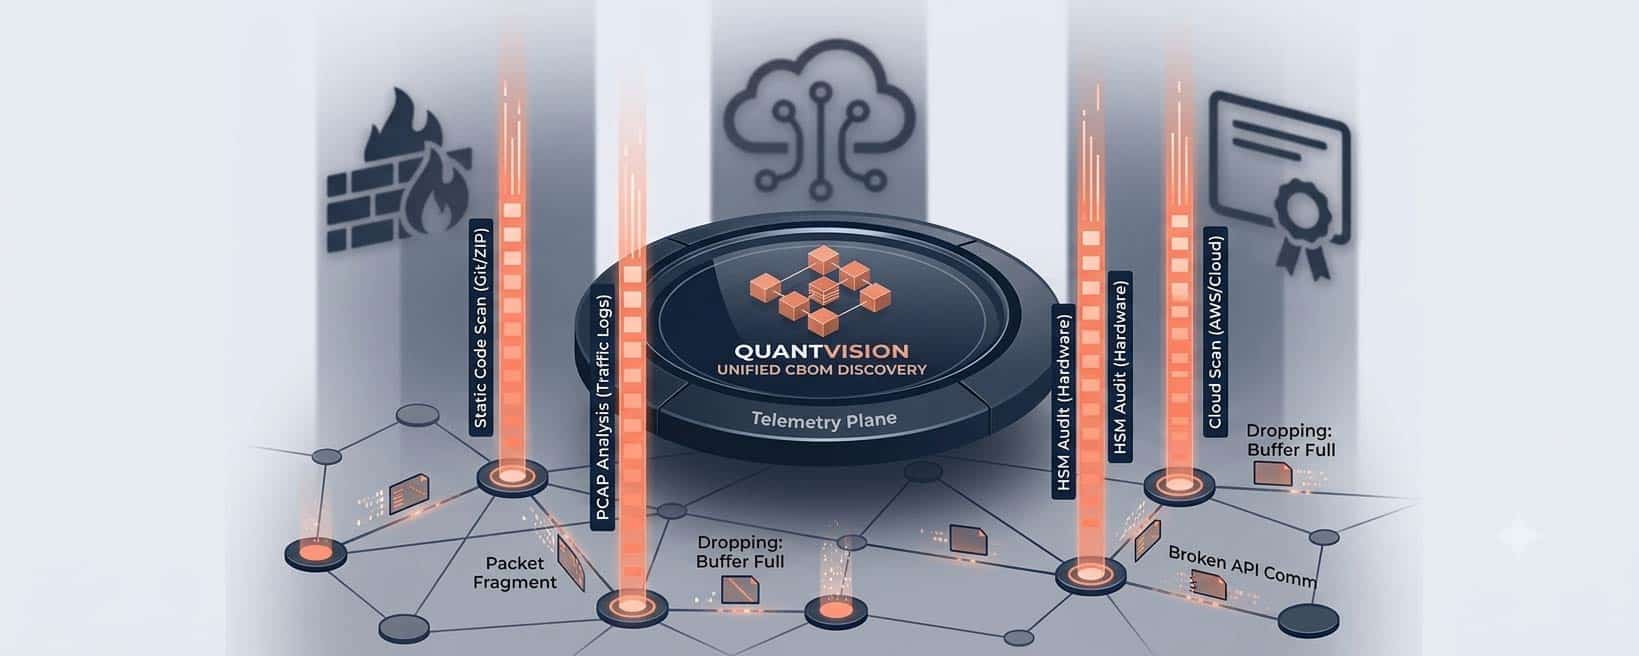
Let’s be brutally honest about the Post-Quantum Cryptography (PQC) migration: No single vendor or magic-bullet tool is going to make your entire enterprise “Quantum Safe” overnight.
With the recent White House Executive Order on PQC and NIST’s finalized standards (FIPS 203, 204, 205), the market is flooded with bold promises. But any experienced CISO or Enterprise Architect knows the technical reality: Cryptography isn’t a single switch … Read More
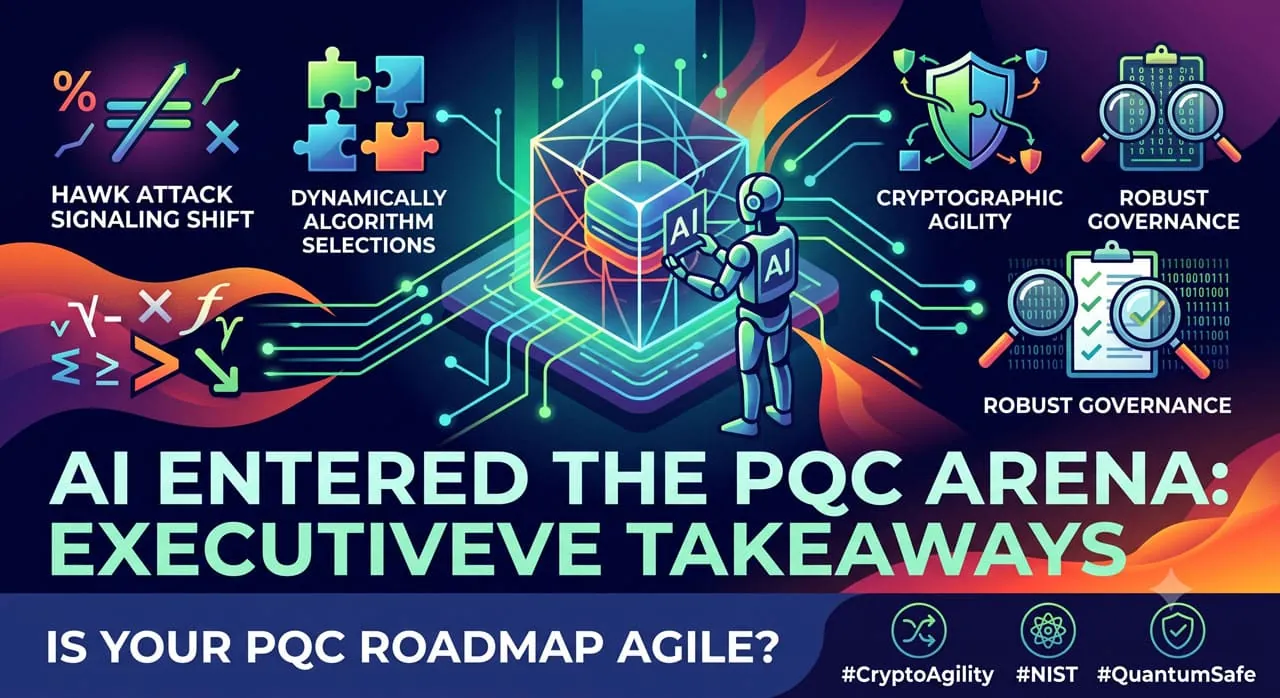
AI Just Entered the PQC Arena – Here Is What Security Executives Need to Know.
Anthropic’s recent preview of Claude Mythos demonstrated AI models semi-autonomously uncovering structural mathematical weaknesses in cryptographic primitives, most notably cutting the effective key strength of HAWK, a round 3 NIST PQC candidate, roughly in half. While HAWK is a candidate … Read More