
On October 7, Surfshark added ML-DSA certificate-based authentication to its WireGuard implementation — completing a migration that started with ML-KEM key exchange “a while back.” The gap between those two dates is the real story for security leaders.
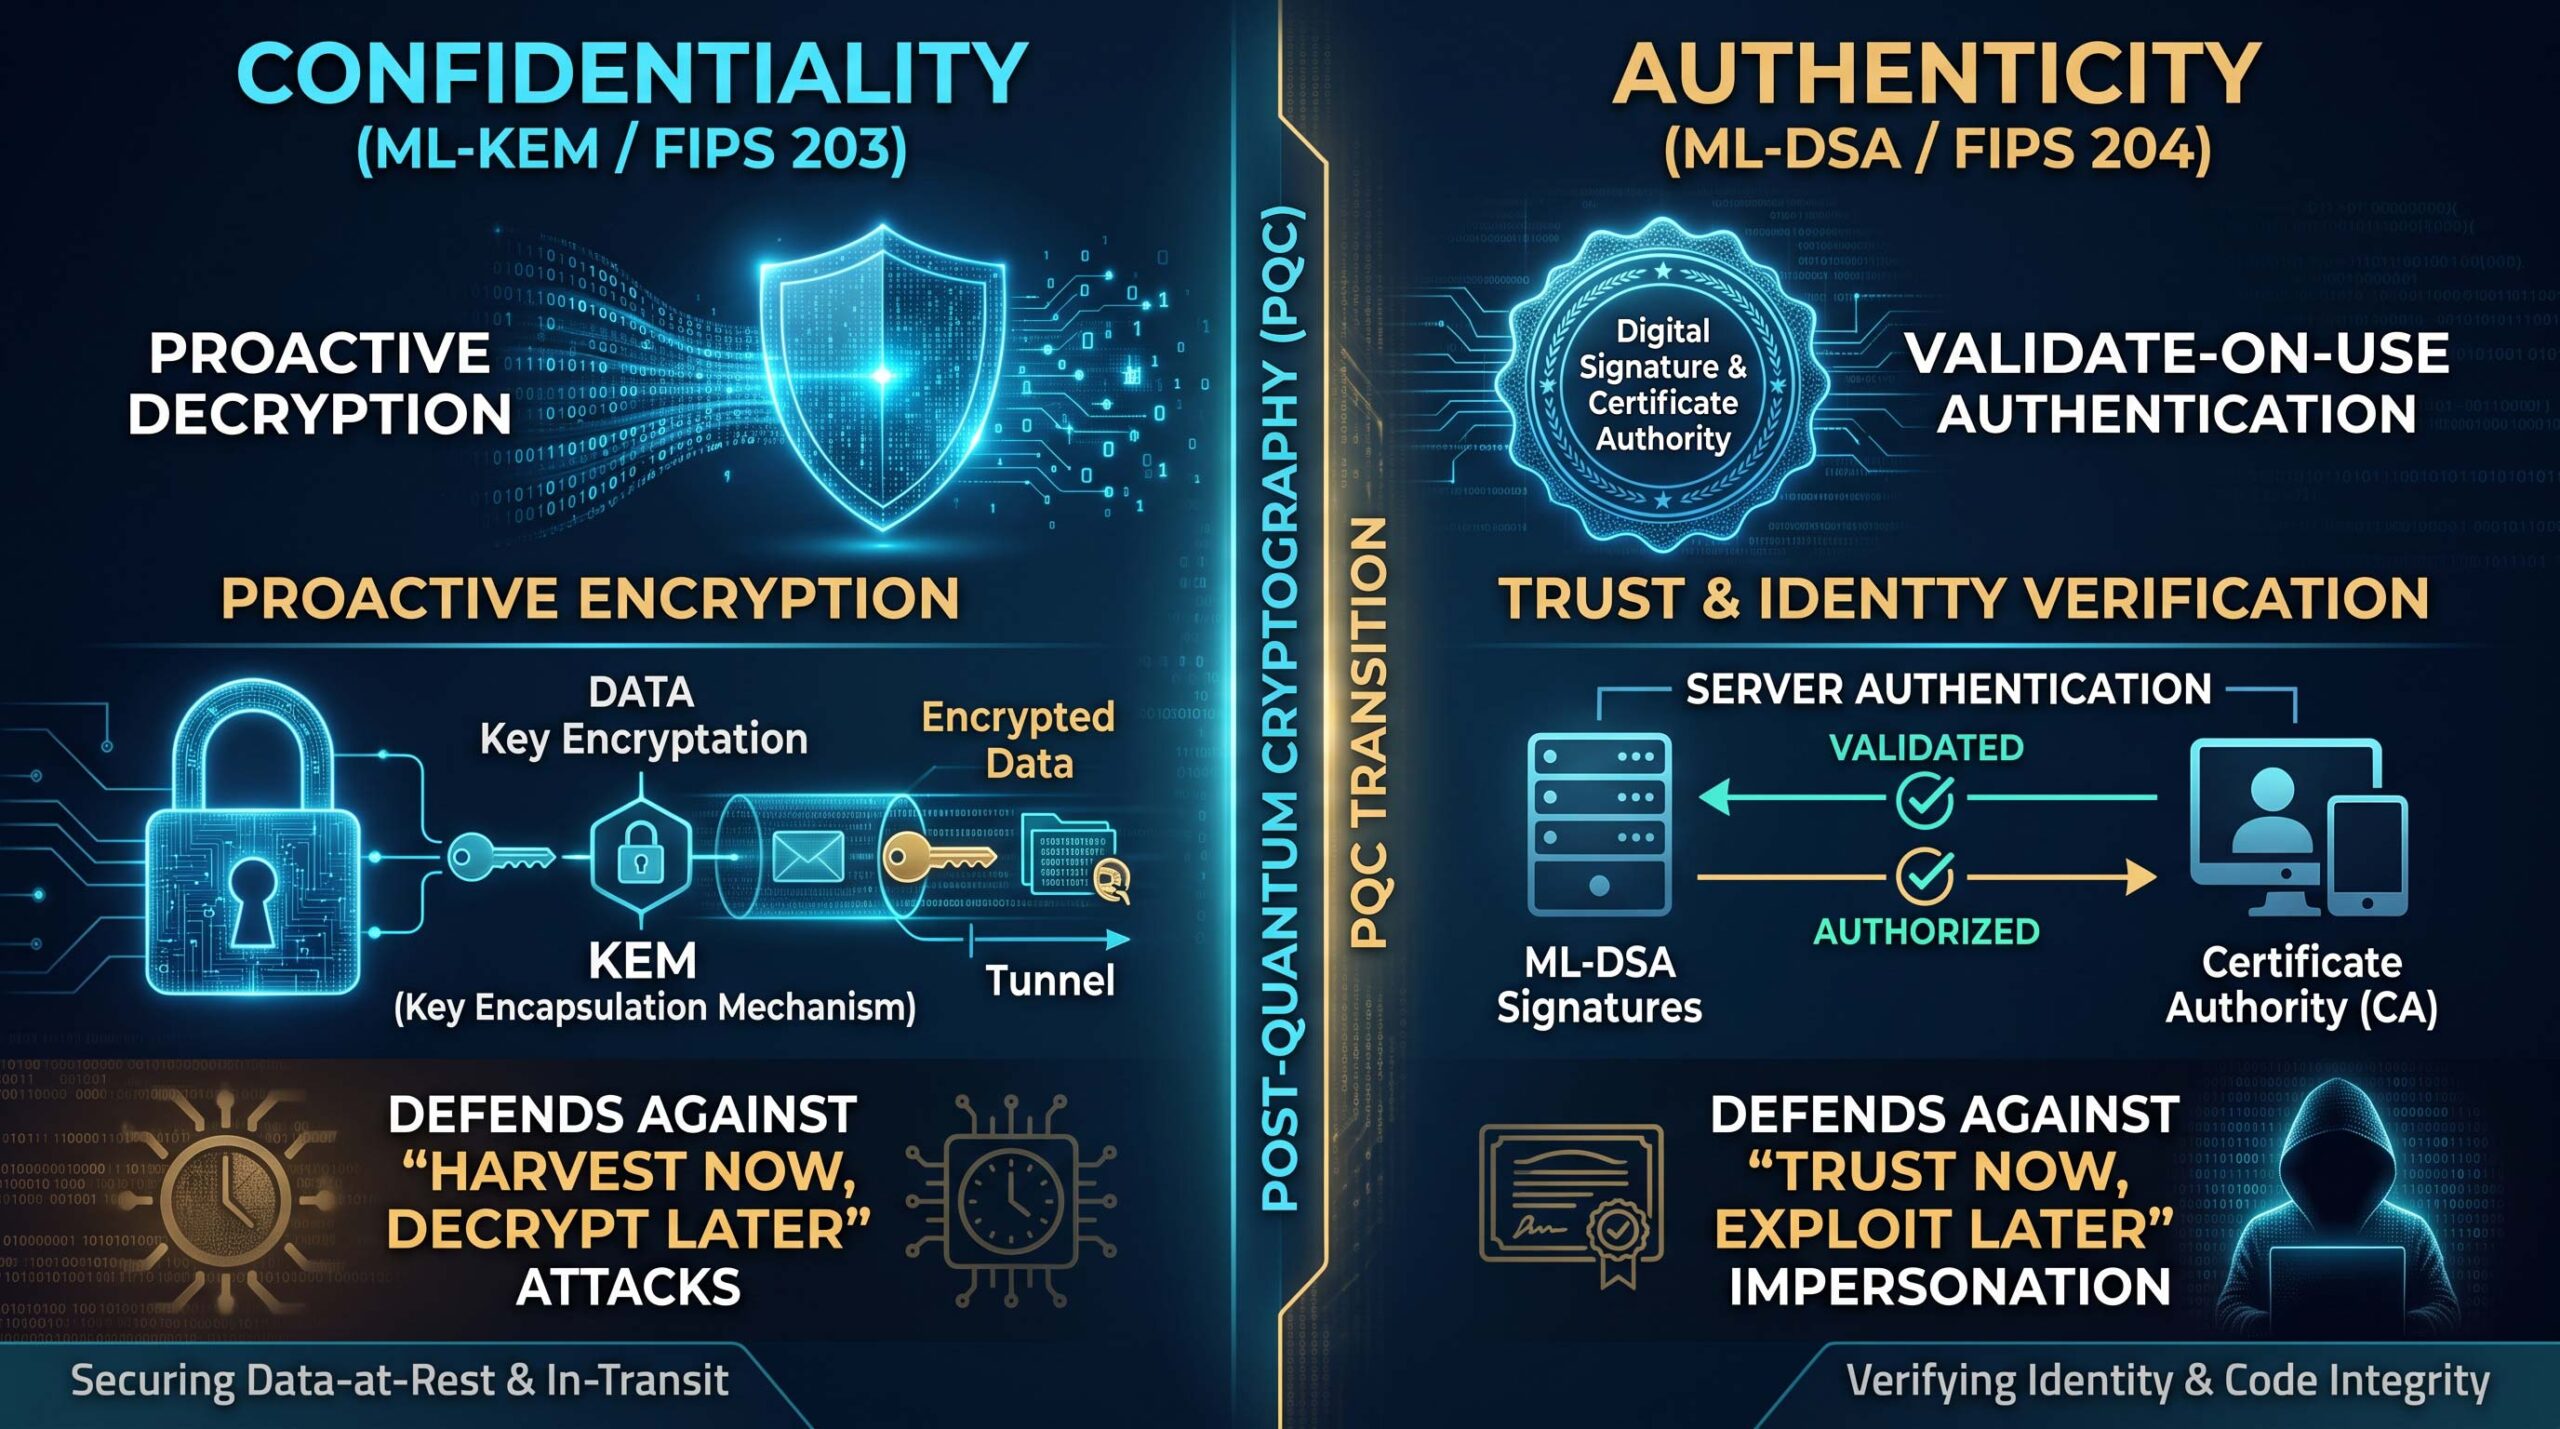
Two algorithms, two different jobs. ML-KEM (FIPS 203) protects confidentiality: it’s what stops an adversary from recording today’s traffic and decrypting it once a quantum computer exists. ML-DSA (FIPS 204) protects authenticity: it’s what proves the server you’re connecting to is actually your server, not a quantum-forged impersonation.
Most “post-quantum” claims are half-true. Surfshark’s own survey of 15 consumer services found 8 had adopted ML-KEM, but only 2 had deployed ML-DSA at all — and both (Google Cloud KMS, AWS KMS) treat it as an optional signing feature customers must enable, not a default. Apple exposes ML-DSA to developers; Microsoft shipped it in Windows. Neither has turned it on for mainstream traffic yet.
Why the timing matters: NSA flagged this exact asymmetry on October 1 — a “trust now, exploit later” threat against code-signing keys, device identities, and certificate authorities, distinct from harvest-now-decrypt-later and arguably harder to retrofit once your PKI is built around classical signatures.
Bottom Line: A crypto inventory that reports “PQC: yes” without separating key-exchange status from signature-algorithm status is giving you false confidence. This is exactly the blind spot QuantVision’s CBOM discovery is built to close — mapping every cryptographic operation it finds by function, confidentiality versus authenticity, not just by algorithm name.
Does your crypto inventory distinguish KEM migration from signature migration, or is “PQC-ready” still one checkbox?
#PostQuantumCryptography #PQC #MLKEM #MLDSA #CryptoAgility #CISO #QuantumSafe #FIPS140 #CNSA2
Sources:
– Surfshark: https://www.google.com/url?q=
– The Quantum Insider: https://www.google.com/url?q=
– NSA background (Oct 1, 2026 “trust now, exploit later” advisory): https://www.google.com/url?q=